
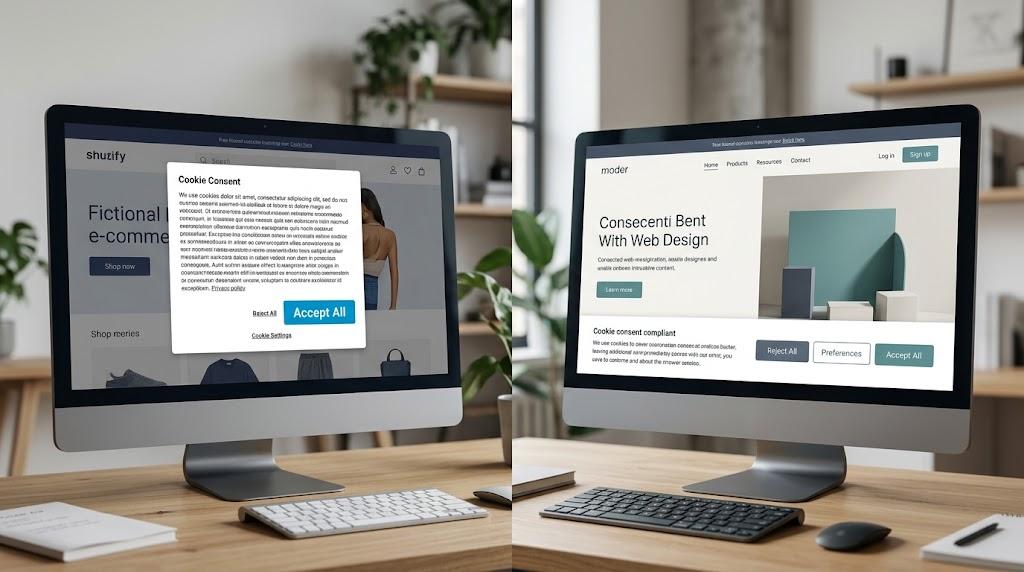
A visitor arrives on your website with a clear purpose. Within seconds, a consent dialog appears and demands they address cookie preferences before proceeding. The content they came for is blocked. The quickest way through is to accept everything, including tracking they never asked for.
This scenario has become so routine that most people now have a reflexive, negative reaction to cookie banners. They associate them with interruption, manipulation, or both.
Anyone building websites professionally knows the tension well. Cookie consent is legally mandatory, but the way most teams implement it creates more harm than good. The regulations themselves are not the problem. The failure is in translation — turning legal requirements into experiences that people find reasonable.
The Regulatory Groundwork You Need to Understand
GDPR took effect in 2018 and applies to any website that processes personal data from individuals located in the European Union. The site's host country is irrelevant. A business operating from the United States with EU visitors falls under the same obligations as one based in Paris. The ePrivacy Directive, widely called the cookie law, addresses the specifics of tracking technologies — cookies, pixels, fingerprinting, and similar tools — and works alongside GDPR.
The core requirement is that tracking cannot begin without the user's explicit, affirmative consent.
What this means in concrete terms is both specific and demanding. Pre-ticked consent boxes are unlawful. If your site deploys optional cookies alongside essential ones, users must be able to choose at the category level — accepting one while declining another. Declining must be no harder than accepting. Any additional step, menu, or configuration screen on the decline pathway violates the standard. Users must also have a persistent, discoverable way to return to their consent choices and revise them.
Enforcement is active and ongoing. EU data protection authorities have imposed major fines for consent violations across a range of industries and company sizes. The European Data Protection Board has issued formal guidance on cookie consent, and national regulators conduct regular audits. Ignorance of the rules does not provide protection.
The Design Patterns That Damage User Trust
A survey of existing cookie banners reveals a disturbing consistency in how they fail users. Three patterns account for the majority of the damage.
Full-screen overlays remain the most aggressive approach. When a consent dialog covers the entire viewport, the visitor has no ability to assess your content, product, or credibility. They are forced into a data-sharing decision without any basis for making it. The message this sends is not subtle: our compliance obligations take priority over your experience. Many visitors respond accordingly — by closing the tab.
The second pattern is visual manipulation of choice. The accept button is designed to dominate. It is large, vivid, and centrally positioned. The reject button is minimized — a small text link, a ghost outline, or an option buried inside a sub-menu. This is not a neutral design choice. It is a dark pattern that leverages visual hierarchy to influence behavior. Regulators across the EU have condemned this practice, and the concept of freely given consent is fundamentally incompatible with it. A professional working with a web design agency is expected to treat equal button treatment as a baseline compliance requirement, not an aesthetic preference.
The third pattern involves what happens when a visitor attempts to customize their choices. Some banners present only an "Accept" option and a "Manage Preferences" button. Clicking the latter opens an extensive configuration panel filled with individual vendor names, legal descriptions, and granular toggles. A typical panel might list fifty or more entries. The process takes time, requires technical literacy, and offers no clear guidance on what each option actually controls. Most visitors who start the configuration process abandon it and click "Accept All" to end the experience. That is not informed, freely given consent. It is a procedural artifact that serves the data controller, not the data subject.
A More Thoughtful Approach to the Consent Interface
Meeting GDPR requirements does not require sacrificing user experience. The two goals align more naturally than most teams assume. Here is what a website designer who takes both seriously focuses on.
Banner size and placement set the foundation. Keep the dialog small. Position it as a bar along the bottom or top edge, a compact card in a corner, or a floating element that overlaps only a small area. The content underneath must remain visible. This is important for a simple reason: a visitor who can see your page forms a reason to stay. That context makes the consent interaction feel like a brief formality rather than an obstacle.
Equal visual treatment of buttons is non-negotiable. The accept and decline options should share the same size, shape, color intensity, typography, and placement. One click should be sufficient to reject all non-essential cookies. If declining requires extra steps, the resulting asymmetry is a dark pattern in practice. The regulation is explicit, and the design must be equally unambiguous.
Language should be direct and brief. One or two sentences explaining what cookies are used for satisfy the informed consent requirement. "We use cookies to remember your preferences and analyze how visitors use our site" communicates the purpose without legal jargon. Visitors who want the full picture can follow a link to your privacy policy. Dense legal prose inside a small dialog achieves nothing except reader fatigue.
Categories should reflect user comprehension, not technical architecture. Organize cookies into a small number of broad groups — essential, analytics, functional, and marketing — each with a toggle. This satisfies the requirement for granular consent without exposing the visitor to your complete vendor inventory. What users want to understand is the type of data being collected and the general purpose, not the specific ad networks operating in the background.
Making the Code Honor the Interface
The banner is a promise. The code beneath it either keeps that promise or quietly breaks it. A web design agency building for compliance treats consent enforcement as a foundational architectural decision.
Begin with a tracking inventory. Identify every third-party script the site loads — analytics platforms, advertising pixels, session-replay tools, social widgets, A/B testing frameworks, chat scripts. Each one constitutes a data collection mechanism that requires consent unless it is strictly necessary for the service the visitor requested. Reducing unnecessary scripts simplifies consent and typically improves page speed.
The critical technical constraint is that no non-essential script may execute before the visitor has granted consent. If an analytics library fires during the initial page load — before any interaction with the banner — the site has processed data without authorization. Engineering teams implement this through consent-aware triggers in a tag management platform or code that checks consent state before loading external resources. Essential functionality like shopping cart session management is exempted.
Reversal must work at the system level. When a user who previously accepted all cookies withdraws consent, the relevant scripts should stop, and stored data should be deleted where feasible. A small "Cookie Preferences" link in the site footer should reopen the consent interface on demand. This mechanism satisfies the GDPR requirement for revisitable consent and belongs in the shared page template, available on every page.
Accessibility Is Not Optional
Cookie banners are interactive web components. Every accessibility standard that applies to buttons, forms, and dialogs applies here without exception.
Keyboard operability comes first. Every interactive element inside the banner must be reachable through the Tab key. A visible focus indicator should be present so keyboard users know where they are in the tab order. Enter and Space should activate the focused control. Any element that cannot receive keyboard focus is an accessibility barrier.
Contrast is a frequent problem. The Web Content Accessibility Guidelines require a minimum contrast ratio of 4.5:1 for standard text. A decline button rendered in a pale color on a white background likely fails this standard. When one option becomes harder to perceive than the other, the disparity functions as a dark pattern regardless of intent. Every text element in the banner — button labels, descriptions, category headers — must meet this threshold.
Semantic structure for screen readers is the final requirement. The banner container should carry the correct ARIA role. Interactive controls need accessible names. When the banner appears, the event should be announced to assistive technology users. Without these attributes, the consent interface is effectively invisible to visitors using screen readers — a failure of inclusive design that carries both legal and ethical consequences.
Post-Launch Testing and Sustained Compliance
Shipping a consent banner marks the beginning of its lifecycle, not the end of the work.
Test in a controlled environment first. Open a private browsing session and load the site. Confirm the banner triggers on the first visit. Walk through every path — accept all, reject all, and customize individual categories. After each interaction, examine browser storage and network requests. Verify that declined scripts are genuinely prevented from executing. A banner that visually hides a tracking pixel but still sends the network request has not achieved compliance.
Mobile testing deserves dedicated attention. Consent interfaces that look perfect on a desktop often fail on a phone. Buttons overlap, text clips, and the dismiss control may be obscured by browser chrome. Evaluate the design at multiple breakpoints. Every tap target should meet the 44 by 44 pixel minimum recommended by both iOS and Android accessibility guidelines. Mobile visitors are not a secondary audience — they represent a significant share of traffic.
Regulations continue to evolve. The EU is advancing additional digital privacy legislation that will reshape consent requirements. The ePrivacy Directive faces ongoing interpretation from the European Data Protection Board and national authorities. State laws like California's CCPA, along with similar frameworks in Colorado, Virginia, and Connecticut, introduce jurisdiction-specific nuances. A web design agency that maintains compliance keeps the consent management platform current with these changes. Proactive adaptation is always less costly than reactive remediation.
The Design Principle That Ties It All Together
Every cookie banner is a communication. It tells the visitor whether your organization views data sharing as a respectful exchange or a compliance checkbox to be cleared.
Blocking the entire page communicates that your obligations outweigh the visitor's experience. Imbalanced buttons communicate that you would prefer they accept without deliberation. Overwhelming complexity communicates that declining is technically possible but practically unreasonable.
A small, balanced, transparent banner communicates something different. It says: here is what we collect, here is why, and here is how to change your mind. That message takes seconds to read and a single click to act on.
Build with restraint. Balance your buttons. Keep the language human. Verify through testing that your code respects every choice the visitor makes. Ensure the path back to those choices is always open and easy to find.
Compliance and thoughtful design do not compete. They converge when the consent banner is treated as a genuine moment of transparency — not a legal formality to be minimized.

 English
 French
 Spanish
 Turkish
 Italiano
 Russian